
We help organizations achieve specific milestones in governance, information technology risk and operational risk, becoming a trusted partner in an evolving digital and geopolitical landscape.
Through focused expertise, judgment and collaboration, we turn insights into practical actions embedded across your organization and owned by your teams.
Our Services
Our offering is grounded in a risk-based approach aligned with recognized frameworks and standards, including COBIT 2019, COSO and ISO 31000, and designed to support operational effectiveness beyond compliance.
Risk & Assurance | IT & OT
Cybersecurity Governance
Cybersecurity governance informed by NIST CSF 2.0 and ISO/IEC 27001:2022 frameworks. We work with organizations at different stages of cybersecurity maturity, supporting a range of governance, risk and assurance needs across their cybersecurity programs.
LeadSecure™ cyber self-assessment
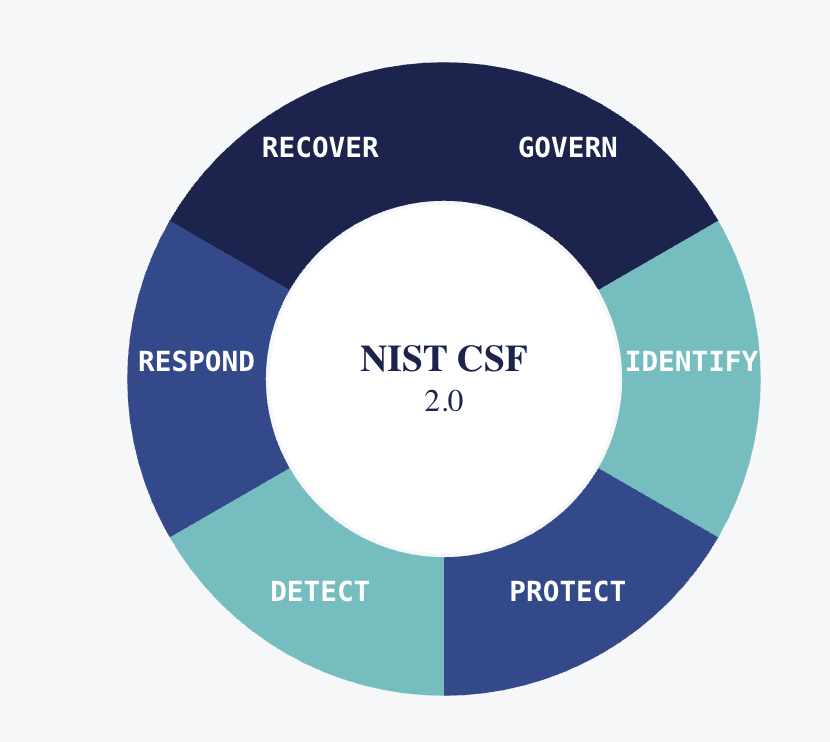
Our LeadSecure™ cyber self-assessment is a simplified adaptation of the NIST CSF 2.0, to help managers and entrepreneurs understand fundamental cybersecurity principles as they begin strengthening their cybersecurity posture.
Why work with us ?
Strategic & Technical Insight
We combine strategic perspective and technical expertise in IT/OT risk, assurance, and cybersecurity governance to support informed decisions.
Focused Expertise
Our services are grounded in proven industry experience, professional credentials, and continuous learning.
Practical Approach
We deliver practical, resource-conscious outcomes that fit your organization's people, processes, and technologies.
Multicultural Perspective
Our experience across North America and Latin America strengthens communication and collaboration across diverse teams and operations.
Explore insights relevant to your organization
Cybersecurity in Operational Technology
Due Diligence for Engaging IT Provider